
The first step is to install Proxychains:
sudo apt update
sudo apt install proxychains
After we have successfully installed Proxychains, we can go ahead and test it.
Open a terminal window and execute the following command:
ssh -fN -C -D 9050 trainees@185.59.93.56 -p2020
Afterwards, run gloCOM in a new ‘developer’ instance with Proxychains:
proxychains /opt/gloCOM/bin/glocom --developer
Now, if we check the REGISTER while logging in through the Proxychains-gloCOM instance, we will see that it is coming from our jump host server's public IP address: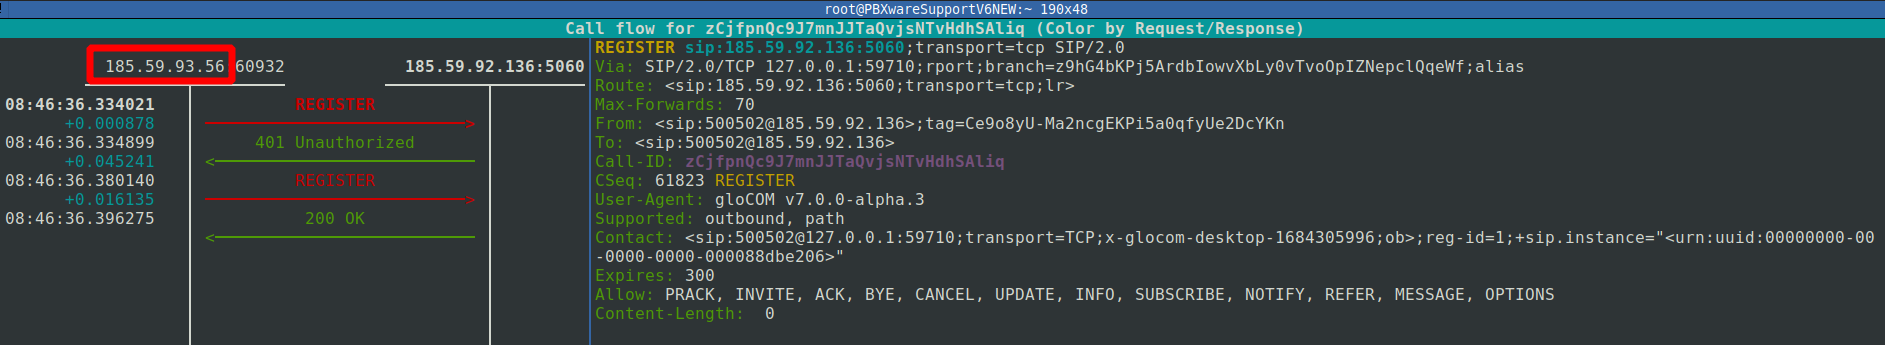
This method is useful in scenarios where customers are reluctant to whitelist anything besides our jump host server and/or you are on a network where your public IP address is changing often.